PDF Version Available
This document is also available in PDF format: malwareanalysis.pdf
The PDF version includes bookmarks for easy navigation and is optimized for printing.
Accessibility Notice
This document is also available in HTML format at:
Link: https://aholdengouveia.name/InfoSec/labs/malwareanalysis.html
The HTML version provides enhanced accessibility features including keyboard navigation, screen reader support, responsive design, dark mode support, and high contrast options.
Learning Outcomes
By the end of this lab, you will be able to:
- Explain how past malware incidents happened, what they caused, and the lessons learned
- Analyze a recent malware attack, including its attack vector, behavior, targets, and impact
- Recommend ways to prevent and reduce malware infections, and explain why they work
- Evaluate sources with the CRAAP test, and show that each one is real
Lab Instructions
You'll write a report of at least 3 and a half pages about malware: two historical incidents, one recent attack, and your recommendations for preventing infections.
What your report must include
Your report must be at least 3 and a half pages, not counting citations, checklists, or screenshots. Include these sections, clearly labelled:
- Two historical malware incidents, about 1 page each: two incidents that had a big impact on security or society, such as Stuxnet or WannaCry. For each one, explain how it happened, its consequences, and the lessons learned. Also say what type of malware it was, such as a virus, worm, trojan, rootkit, or ransomware, and explain how you decided.
- A recent malware attack, about 1 page: an attack from the last 2 years. Explain the attack vector, how the malware behaved, who or what it targeted, and its impact on the people, organizations, or governments affected. Also say what type of malware it was, and explain how you decided.
- Recommendations, about half a page: best practices for preventing and reducing malware infections, such as antivirus software, network security, and user education. Explain why each one helps.
- Putting it into practice: explain how your recommendations would apply to your own devices, your school, or a workplace you know. Be specific.
Malware types: for all 3 of your malware examples, decide the type based on how it spread and what it did. For example, a worm spreads on its own, and a trojan hides inside a program that looks safe. Some malware is more than one type. WannaCry was ransomware that spread like a worm, so name every type that fits. Back up each choice with a source that describes the malware that way, and cite it in the sentence.
Sources
You need at least 5 sources, including at least one dated source about your recent attack. For each source, include:
- A citation, in APA or MLA style. If you want to use another style, check with me first.
- A CRAAP test checklist or paragraph: Currency, Relevance, Authority, Accuracy, and Purpose.
- A screenshot of the source, showing its title and date.
- One direct quote from the source, and where it appears, such as the paragraph, section, or page.
Citing in your report:
- Anything you copy word for word is a quote. Put it in quotation marks and cite it.
- Anything you reword, or take the ideas from, still needs a citation.
- Ideas you've put together from several sources in your own words don't need a citation in the sentence, but the sources must be in your source list.
Screenshots
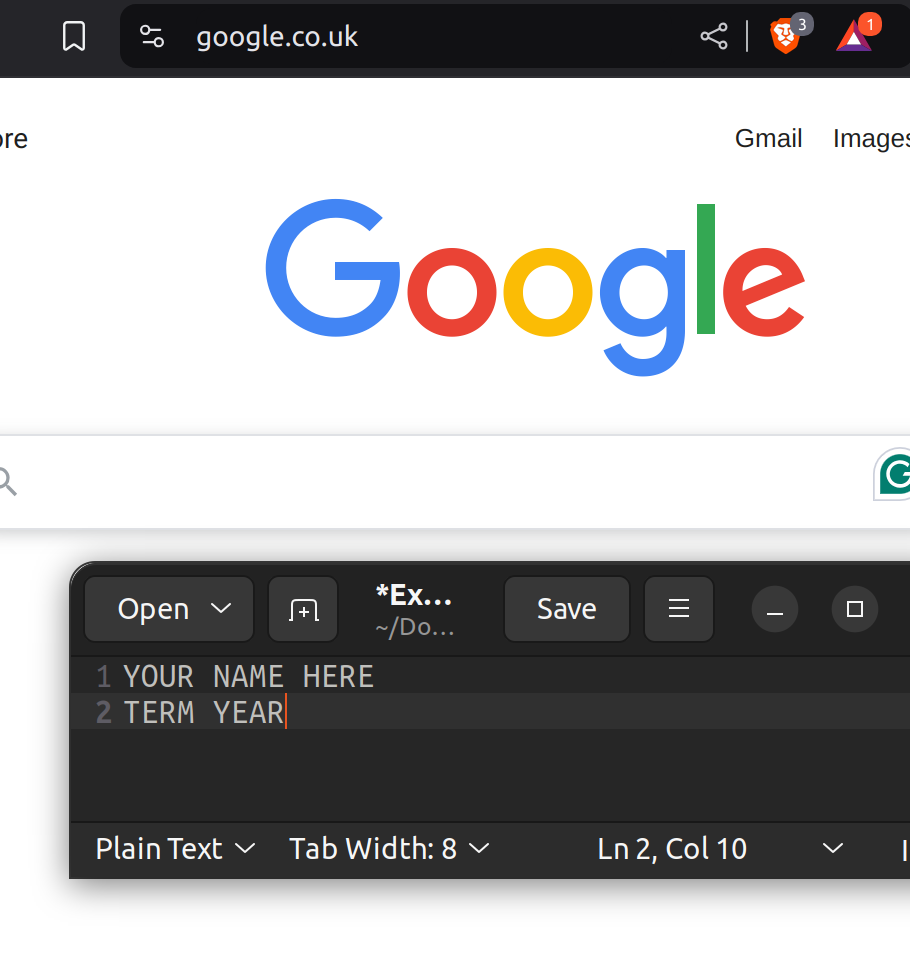
Each screenshot should have your name, term, and year. One of the easiest ways to do that is make a text document with your name and term/year on your computer and save it to use all term. Any screenshots that don't include this information won't be counted.
Deliverables
One file that includes:
- Your report, with all 4 sections clearly labelled
- Your source list, with a CRAAP check, a screenshot, and a direct quote for each source
The CRAAP checks, screenshots, and quotes can go at the end of your report.
Resources
References, a video, a PowerPoint and some notes are available at my website Link: https://www.aholdengouveia.name/InfoSec/Malware.html
My guide to evaluating sources Link: https://www.aholdengouveia.name/Howtos/Sourceeval/sourceEvaluation.html
The CRAAP test, with questions to ask about each source Link: https://web.archive.org/web/20250814000638/https://guides.lib.uchicago.edu/c.php?g=1241077&p=9082343
Another explanation of the CRAAP test Link: https://libguides.butler.edu/c.php?g=117303&p=1940068